Towards Insider Threat Resilience: A Proposed Mitigation Model
At a glance
| Problem | Insiders already have access, so they can copy sensitive files out of the company. |
|---|---|
| Idea | Bundle every protected file with a hidden check. The file opens only on approved networks. |
| Result | On the office network the file opens normally. On any other network its contents are erased. |
| Built | A Windows app in Flutter and Dart that generates the protected file |
| Tech | Flutter, Dart, Python, PyInstaller, self-extracting archive (steganography) |
| Published in | 2024 International Conference on Emerging Systems and Intelligent Computing (ESIC) |
| Where & when | February 2024 · Bhubaneswar, India |
| Publisher | IEEE (2024) |
| DOI | 10.1109/ESIC60604.2024.10481615 |
How it works
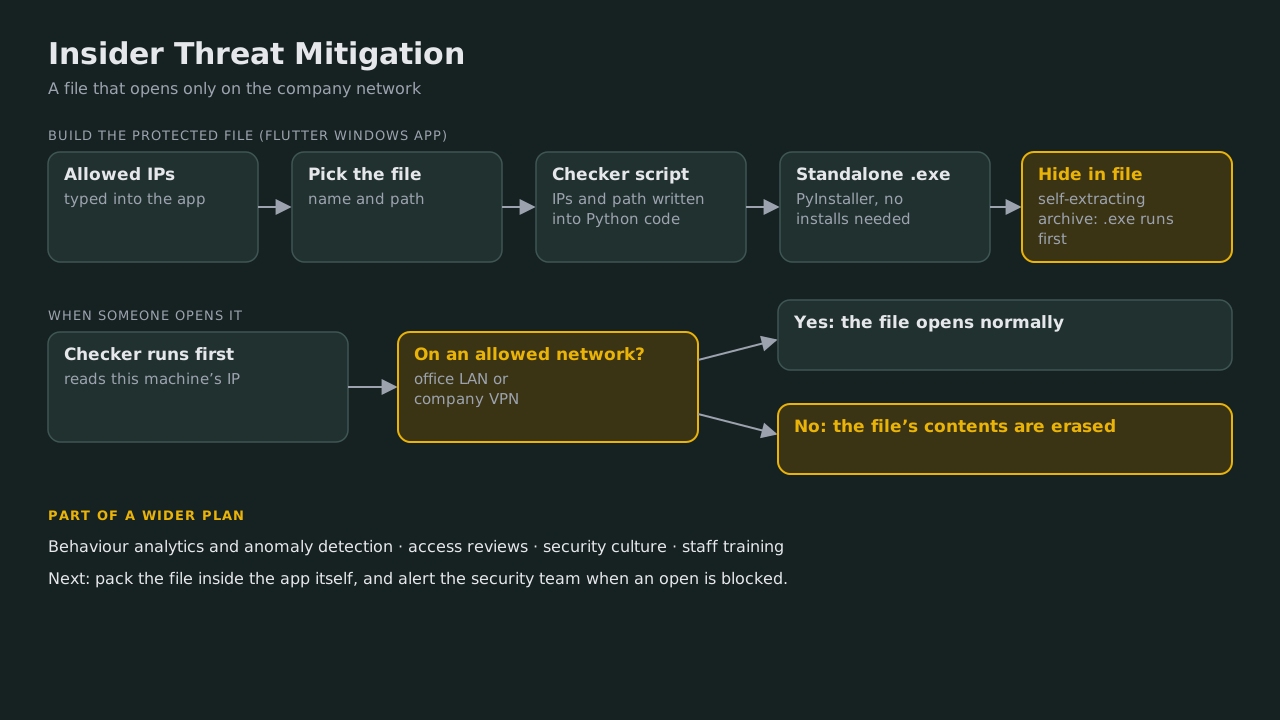
- Enter allowed IPsFlutter app
- Pick filepath saved in script
- Build .exePyInstaller
- Hide in fileself-extracting archive
- OpenedIP allowed? open : erase
Key points
- Enter the allowed network IPs and pick the file to protect in the app
- The app writes those IPs and the file path into a Python checker script
- The script is turned into a standalone .exe, so the target PC needs nothing installed
- The .exe and the file are packed into one self-extracting file that runs the check first
- Works for remote staff too, as long as they connect through the company VPN
Results
| Where it is opened | Result |
|---|---|
| Office network | Opens normally |
| Company VPN (remote staff) | Opens normally |
| Any other network | Contents erased |
Architecture
More numbers and details
- The paper also covers the wider plan: behaviour analytics, anomaly detection, access reviews, security culture and training
- Steganography here means hiding the checker inside the file you share
- Next steps: build the packing step into the app, and alert the security team on a blocked open
- Cybersecurity
- Insider Threat
- Steganography
- Data Leak Prevention
- Flutter